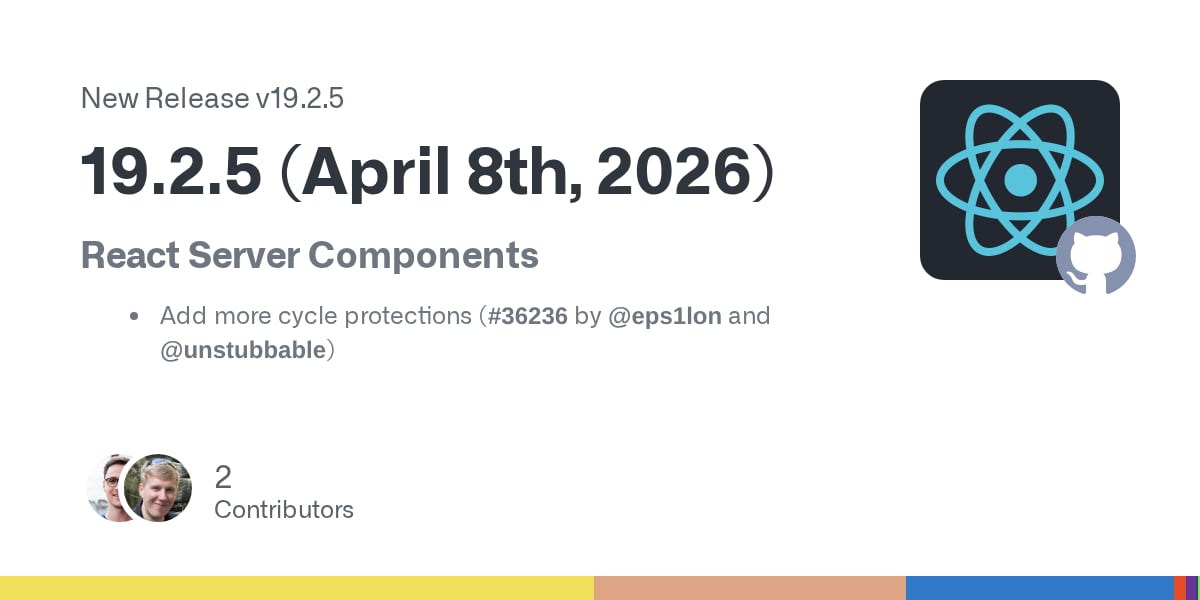
React 19.2.5 went out on April 8 with a single change: more cycle protections for React Server Components. The same fix shipped as 19.1.6 and 19.0.5 the same day, which is the pattern React uses when a fix matters to every supported line.
By my count it is the third round of Server Components hardening in four months. December brought loop protection for Server Functions. January brought denial of service mitigations for Server Actions and further hardening of Server Components. Now cycle protections. None of these are large releases, and that is the point.
Here is what I think changed for front-end teams. A client-side React app had a security surface that mostly belonged to someone else: the browser, the server team, the gateway. Server Components move part of React onto the server, where it deserializes input that came from a network. That is a different class of surface, and it comes with a different class of patch, the kind that has to be in production within days, not in the next planned upgrade.
My view is that a team adopting Server Components has to decide, on purpose, who watches for these releases and how fast they ship. It is not a hard job. It is a job that does not happen unless someone has it.
Who on your team would notice a React patch release the day it came out?
Photo source: https://photos.robertstowe.com/flowers